Article

Gap Assessments: Your Security Starting Point

OT Cybersecurity Gap Assessments: The First Step Toward a Safer, More Reliable Operation 

For industrial organizations, building a mature cybersecurity posture starts with clarity. You can’t improve what you can’t see, especially in complex OT environments where aging systems, undocumented devices, and day-to-day operational pressures create blind spots. 

A gap assessment gives OT teams that clarity. By comparing your current controls, policies, and procedures against frameworks like NIST CSF, ISA/IEC 62443, or NERC CIP, it delivers a clear, prioritized roadmap tailored to your operations. For operators, technicians, and engineers, the impact is direct: improved uptime, reliability, safety, and long-term system health. 

What an OT Gap Assessment Is and Why It Matters 

A gap assessment evaluates your OT environment against a defined target state built on industry standards, regulatory requirements, and operational needs. It enables you to understand: 

  • Your true security posture 
  • Operational weaknesses tied to legacy systems or manual processes 
  • Misalignments between policy and reality 
  • The highest-impact improvements to reduce risk 

OT systems can’t simply be rebooted or patched whenever convenient. Every change must protect safety, reliability, and process continuity and a gap assessment ensures your controls and processes support those realities. 

For OT personnel, the benefits include: 

  • Better visibility into aging and undocumented assets 
  • Reduced troubleshooting time 
  • Increased confidence in system reliability 
  • Early insight into modernization and lifecycle requirements 
  • Stronger justification for budget and resource planning 

A gap assessment shifts the conversation from “Is our firewall configured correctly?” to “Do our systems and processes support long-term operational health and safety?”

What to Expect During the Assessment 

The process is collaborative and designed to minimize operational disruption. It focuses on how your facility actually works, not just what’s documented. 

Typical activities include: 

  • Documentation Review: Architecture diagrams, control system configurations, network designs, and backup procedures 
  • Field Validation: Walkdowns in control rooms, server cabinets, and field panels to verify what actually exists 
  • Workflow & Access Review: Operator practices, account usage, change management, and legacy “tribal knowledge” 

The goal is a clear, accurate understanding of your current environment. 

Key Components of an OT Gap Assessment 

1. Baseline Evaluation 

We document how systems are designed and operated today, capturing real-world conditions such as unsupported operating systems, end-of-life controllers, unmanaged network devices, vendor-installed assets, and manual processes that introduce operational risk. 

2. Target State Definition 

Together, we establish a realistic target state aligned with NIST CSF, ISA/IEC 62443, regulatory obligations, and your operational priorities. 

3. Gap Identification 

We highlight where your environment diverges from best practices across segmentation, access control, backups, patching, monitoring, governance, and system lifecycle practices and explain what each gap means for uptime, safety, and reliability. 

4. Remediation Planning 

We build a prioritized roadmap that accounts for downtime windows, staffing, investment needs, and alignment with ongoing modernization efforts. Every recommendation is practical for a 24/7 industrial environment. 

What We Typically Find and Why It Matters 
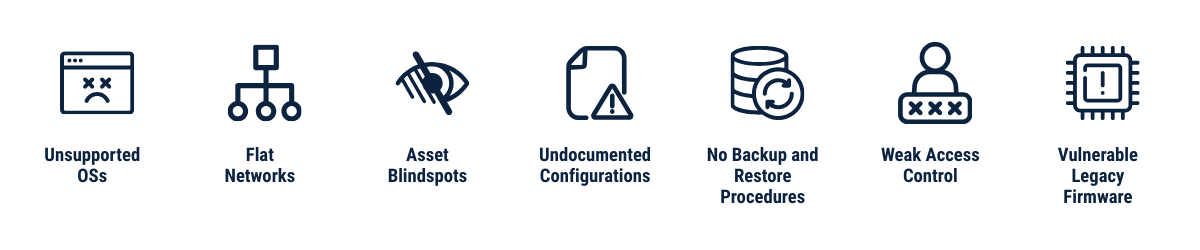
Across assessments, common issues include: 

  • Unsupported or unpatched operating systems 
  • Flat networks with limited segmentation 
  • Outdated or incomplete asset inventories 
  • Poorly documented configurations 
  • Lack of formal backup/restore procedures 
  • Shared accounts or unmanaged access 
  • Legacy firmware with known vulnerabilities 

These conditions are typical in long-lived OT systems. A gap assessment simply makes them visible so improvements can be planned objectively and cost-effectively. 

Key Takeaway 

A gap assessment is the foundational step toward building a resilient OT cybersecurity and operational program. It provides clarity, actionable priorities, and a realistic roadmap grounded in your operational reality. 

For OT end users, it delivers what matters most: safer operations, fewer disruptions, and a more reliable control system environment. 

🏆The Champion Advantage

We don't just assess, we also implement remediations. Many firms can identify gaps, Champion closes them. 

Deep OT Expertise 

Our engineers understand legacy and modern control systems across PLC, DCS, SCADA, networking, virtualization, and system architecture. 

From Findings to Implementation 

We don’t stop at recommendations. Our teams execute the remediation work, whether that means: 

  • Segmenting networks 
  • Deploying firewalls or access control improvements 
  • Updating or migrating control systems 
  • Virtualizing servers 
  • Implementing backup/DR solutions 
  • Replacing outdated PLCs or infrastructure 
  • Supporting DCS modernization or on-process migrations 

You get a partner who can take your roadmap from paper to production. 

Proven in Live Industrial Environments 

Our methodology has been refined across various critical infrastructure industries, without jeopardizing operational continuity. 

Integrated Support 

We work closely with operators, engineers, and IT/OT teams to ensure every improvement aligns with real workflows, staffing, and maintenance constraints. 

Your assessment becomes a fully supported execution plan, not homework. 

How Gap Assessments Support Modernization 

Many organizations begin with a gap assessment before embarking on broader modernization efforts like: 

  • DCS upgrades 
  • Virtualization 
  • On-process migrations 
  • Network redesigns 
  • OT data center development 

By identifying aging assets, unsupported software, and high-risk configurations early, the assessment ensures modernization plans are cleaner, safer, and more cost-effective.

Let's collaborate.

Schedule a no-cost consultation today.


Article

A Guide to Cybersecurity Assessments


More Posts
Read More
Article

Mastering OT Asset Monitoring

🛠️ Optimizing Uptime Through OT Monitoring

As industrial OT systems modernize and become more interconnected, the potential for efficiency and insight grows, but so do complexity and cybersecurity risk. To navigate this landscape, organizations must move beyond reactive maintenance and adopt a layered, proactive monitoring strategy.

🔍 Three Pillars of Modern OT Monitoring

Just as a skilled technician uses multiple tools to assess a system, a modern OT monitoring strategy relies on three complementary methods: passive, active, and predictive. When combined, they create a robust defense and operational advantage.

Passive Monitoring

The Silent Observer of OT Health

Passive monitoring silently collects data from systems without direct interaction. It captures the "background noise" of OT—CPU usage, network traffic, system logs—offering insights without introducing risk.

Use Cases:

  • Baseline Behavior: Define normal operating parameters to detect future anomalies.
  • Capacity Forecasting: Plan infrastructure scaling based on usage trends.
  • Performance Trends: Spot degradation or irregularities early.
  • Asset Visibility: Maintain a real-time inventory of connected OT assets.

Active Monitoring

Probing for Responsiveness and Resilience

Active monitoring takes a deliberate, hands-on approach. By sending test traffic or running diagnostics, it probes systems to detect weaknesses or performance bottlenecks.

Use Cases:

  • Early Issue Detection: Identify misconfigurations or failing components.
  • Network & Application Tuning: Support digital initiatives with optimized performance.
  • Cyber Vulnerability Scanning: Detect threats across newly connected assets.
  • Regulatory Readiness: Validate compliance with industry standards.

Predictive Monitoring

Anticipating What's Next

Predictive monitoring applies analytics and machine learning to historical and real-time data to forecast problems before they occur.

Use Cases:

  • Predictive Maintenance: Anticipate equipment failures and plan service proactively.
  • Resource Planning: Forecast compute and bandwidth needs as systems scale.
  • Anomaly Detection: Flag unusual activity that could signal cyber threats.
  • Downtime Reduction: Improve system uptime and reliability through foresight.

⚖️ Why the Blend Matters

Each technique brings value, but together they form a resilient and intelligent monitoring ecosystem:

  • Passive reveals system norms and long-term trends.
  • Active exposes immediate issues and security gaps.
  • Predictive enables preemptive action to avoid disruptions.

Conclusion

In a digital-first OT landscape, monitoring must evolve. A layered strategy, passive for visibility, active for control, and predictive for foresight, empowers industrial organizations to maintain uptime, ensure security, and drive operational excellence. It’s not just about watching your systems; it’s about truly understanding them.

more on our website

24UP® Solutions


Let's collaborate.

Schedule a no-cost consultation today.


More Posts

Read More
Article

Sustaining Success: Proactive Maintenance for Long-Term Performance

The true value of an Operational Technology (OT) modernization project is realized long after the go-live date. Ongoing maintenance and optimization are essential to sustaining the health, security, and performance of modernized systems. This phase focuses on building a methodology and culture of proactive maintenance, embedding the practices, tools, and mindset needed to protect your investment and sustain long-term operational performance. 

Enabling a Culture of Proactive Maintenance

The Run & Maintain phase marks the shift from maximizing uptime and production. Instead of resolving issues that disrupt production, proactive maintenance anticipates problems before they occur. This approach is enabled by Champion’s 24UP® Solutions, which combine continuous monitoring, analytics, and targeted improvement strategies. 

  • Condition-Based Monitoring: 24UP® implements real-time monitoring of system performance and health. Using data analytics, early signs of degradation are detected, allowing for condition-based maintenance and eliminating costly unplanned downtime. 
  • Reliability-Centered Maintenance (RCM): Maintenance activities are prioritized by asset criticality and failure risk, ensuring resources focus on the systems most vital to safety, production, and compliance. Data from control systems, historians, and sensors supports reliability metrics to guide decisions. 
  • Continuous Improvement: Maintenance doesn’t mean standing still. Through 24UP®, opportunities are continually identified to optimize control strategies, enhance efficiency, and introduce new features that drive added value from your assets. 

Sustaining Security, Compliance & Performance

A modernized system is only as secure and sustainable as its maintenance program. With evolving cyber threats, regulatory requirements, and technology changes, sustaining reliability requires continuous vigilance and structured lifecycle management. 

  • Vulnerability & Patch Management: 24UP®  enables a disciplined process for vulnerability scanning and patch deployment, tailored specifically for OT environments. Systems remain secure and compliant without disrupting critical operations. 
  • Compliance & Configuration Management: Regular audits confirm alignment with ISA/IEC 62443, NIST CSF, and corporate cybersecurity policies. Configuration backups, user-access reviews, and change-control logs ensure the environment remains both secure and supportable. 
  • Lifecycle & Obsolescence Planning: Clear visibility into hardware and software lifecycles allows for proactive planning of upgrades and replacements, reducing exposure to unsupported technologies and avoiding last-minute procurement challenges. 
  • Spare Parts & Asset Health Management: 24UP®  tracks asset condition and spare-inventory status, helping facilities avoid downtime due to unavailability of critical components. 

Integrating People, Process & Technology 

Technology alone doesn’t sustain performance, people do. Champion’s maintenance approach aligns operators, engineers, and maintenance staff around shared visibility and accountability. 

  • Operator Training & Knowledge Retention: Continuous upskilling ensures operators remain confident with modern interfaces and procedures, strengthening both safety and performance. 
  • Collaboration & Knowledge Capture: Maintenance activities and troubleshooting insights are digitally documented, preserving institutional knowledge for future teams. 
  • Integrated Workflows: 24UP® can interface with enterprise asset-management (EAM) systems such as SAP PM or Maximo, ensuring maintenance coordination and visibility across departments. 

The Champion Advantage

A successful modernization doesn’t end at commissioning; it evolves into sustained performance. Champion’s 24UP® Solutions transforms traditional “break-fix” maintenance into a proactive lifecycle-management strategy that drives long-term value. 

By combining real-time visibility, cybersecurity vigilance, and continuous improvement, 24UP® helps organizations: 

  • Extend asset life and reliability 
  • Maintain compliance and security 
  • Optimize performance and efficiency 
  • Empower personnel through shared insight and training 

Modernization is sustained through performance, and Champion can help you achieve your goals, long after the project is complete. 

Let's collaborate.

Schedule a no-cost consultation today.


more on our website

24UP® Solutions


More Posts

Read More
Project Brief

Multi-Site OT Cybersecurity Assessment

  • The Challenge

The client sought to gain deeper visibility and control across multiple industrial facilities. While each facility had its own systems and processes in place, there was a clear opportunity to enhance standardization, improve documentation, and align cybersecurity practices across the broader OT environment.

Key focus areas included:

  • Establishing a consistent view of OT assets across all facilities
  • Improving clarity around existing network architectures
  • Identifying opportunities to strengthen and unify cybersecurity policies and controls

With this assessment, the client aimed to lay a stronger foundation for long-term resilience and scalable security management.

  • Our Solution
Asset Inventory and Lifecycle Analysis

Champion conducted a thorough inventory of OT assets across all sites, capturing:

  • Detailed information such as make, model, and operational condition
  • Lifecycle stage and support status
  • Physical location and criticality
Network Topology Mapping

We mapped each site’s Process Control Network (PCN), delivering:

  • Accurate, facility-specific network diagrams
  • Visibility into asset interconnectivity and data flow
  • Identification of segmentation gaps and vulnerability points
OT Cybersecurity Gap Assessment and Remediation Planning

Our team performed an in-depth gap analysis and developed a tailored remediation strategy. Key deliverables included:

  • A prioritized list of findings ranked by criticality and operational risk
  • High-level cost estimates for remediation at each facility
  • A strategic roadmap aligned with NIST CSF and industry best practices
  • Project Timeline

4 Months

  • The Results

Champion provided a comprehensive view of the client’s multi-site OT environment, highlighting both areas of strength and opportunities for improvement. Results included:

  • Detailed documentation of assets and network architecture
  • Clear recommendations to formalize cybersecurity policies and procedures
  • Actionable improvements to strengthen monitoring, analytics, and system defenses

We also mapped the client’s position within the NIST Cybersecurity Framework maturity model and delivered prioritized, cost-estimated recommendations. This enabled the client to confidently invest in the most impactful improvements and advance their OT cybersecurity program with clarity and direction.

  • The Champion Advantage
OT Application Expertise

Champion brings deep expertise of both operational technology (OT) environments and enterprise-level network architectures. Our team bridges the IT/OT knowledge gap by:

  • Applying strategies that align with enterprise-wide policies while addressing the unique challenges of OT environments
  • Combining technical depth with hands-on operational experience to reduce risk and improve system resilience
Optimized Integration

Whether upgrading legacy platforms or implementing new technologies, Champion delivers seamless, cost-effective integration. Our proven approach ensures:

  • Interoperability across modern and legacy systems with support for multi-vendor environments

  • Minimal operational disruption through careful planning and phased execution

  • Sustainable, scalable solutions that deliver long-term value and adaptability

article

Securing Legacy OT Systems

solution brief

Disaster Recovery

Read More
Article

A Guide to Cybersecurity Assessments

The Imperative of Proactive Assessments

As industrial environments evolve and IT-OT convergence accelerates, the need for robust cybersecurity grows more urgent. For organizations managing ICS, SCADA, PLCs, and other operational technologies, a compromised system can halt production, endanger safety, and result in regulatory penalties.

Think of cybersecurity assessments as proactive health checks for your control systems. No single test can capture the full picture, each assessment reveals a unique dimension of your cyber risk. When integrated, these assessments form a layered approach that strengthens resilience and guides continuous improvement.

Let’s explore the key assessment types, beginning with the most foundational: the Gap Assessment.

1. Gap Assessment

Gap assessments compare your current cybersecurity state to a defined target, such as regulatory frameworks, industry standards, or internal security policies, to identify specific areas of improvement.

📋Key Components

  • Baseline Evaluation – Establishes the current technical and procedural posture.
  • Target Definition – Defines the expected or required state (e.g., NIST CSF, IEC 62443).
  • Gap Identification – Pinpoints missing controls, insufficient practices, or misaligned documentation.
  • Remediation Planning – Outlines concrete steps to close the gaps.

💡Key Takeaway

Gap assessments are the starting point for any effective cybersecurity improvement plan, revealing exactly what needs to change and helping prioritize remediation.

2. ICS Risk Assessment

This foundational assessment identifies and evaluates risks across your OT environment. It focuses on potential threats, existing vulnerabilities, and the business impact of a successful cyber attack.

📋Key Components

  • Asset Identification – Cataloging ICS components (PLCs, RTUs, HMI, SCADA).
  • Threat Identification – Profiling external and internal threat actors.
  • Vulnerability Discovery – Spotting gaps in systems, processes, and configurations.
  • Impact Analysis – Estimating operational, safety, and financial consequences.
  • Risk Prioritization – Ranking risks to guide mitigation efforts effectively.

💡Key Takeaway

Provides a strategic roadmap to prioritize cybersecurity investments and close high-impact gaps.

3. Vulnerability Assessment

A vulnerability assessment systematically identifies weaknesses, both technical and physical, across your OT environment. It focuses on discovering flaws that could be exploited by threat actors, whether through software vulnerabilities or on-site security gaps.

🔧Key Components

  • Automated Scanning – Identifies known technical vulnerabilities in software, firmware, and network configurations (e.g., unpatched systems, default credentials).
  • Manual Review – Expert analysis of configurations, network architecture, and system documentation to uncover issues not flagged by automated tools.
  • Physical Security Inspection – Assesses physical vulnerabilities such as:
    • Unsecured or poorly located control panels and field devices
    • Inadequate facility access controls (e.g., badge systems, door locks)
    • Lack of surveillance or intrusion detection in critical zones
    • Exposure to environmental hazards (e.g., dust, moisture, vibration)
  • Reporting – Comprehensive documentation of all identified vulnerabilities, including severity ratings and prioritized remediation steps.

💡Key Takeaway

By identifying both cyber and physical weaknesses, this assessment enables a holistic approach to reducing the attack surface and improving overall OT system integrity.

4. Penetration Testing (Pen Testing)

Pen testing simulates real-world attacks to uncover exploitable weaknesses and test the efficacy of defenses.

⚠️Note: OT pen testing must be carefully scoped and is often conducted in lab environments or during maintenance windows to avoid disruption.

Pen Test Types

  • Black Box – Simulates an external attacker with no prior access.
  • White Box – Emulates an insider with full system knowledge.
  • Grey Box – Mimics a partially informed attacker.

🔧Key Components

  • Controlled Exploitation – Validates vulnerabilities without disrupting operations.
  • Lateral Movement Analysis – Identifies possible attack paths within your network.
  • Comprehensive Reporting – Details exploitation paths and remediation priorities.

💡Key Takeaway

Pen tests validate real-world defenses and identify weaknesses that could lead to operational compromise.

5. Compliance Assessment

Compliance assessments evaluates your adherence to industry standards and regulations such as ISA/IEC 62443, NIST CSF, or NERC CIP.

📋Key Components

  • Policy & Documentation Review – Assesses alignment with standards.
  • Technical Control Evaluation – Verifies implementation of security measures.
  • Regulatory Gap Identification – Detects compliance shortfalls.

💡Key Takeaway

Supports regulatory alignment, audit readiness, and stakeholder confidence.

6. Cybersecurity Maturity Assessment

Benchmarks your cybersecurity program against recognized maturity models and identifies paths for structured development.

📋Key Components

  • Process & Capability Evaluation – Across risk management, incident response, access control, etc.
  • Benchmarking – Against industry best practices or target maturity levels.
  • Improvement Roadmap – Tailored actions to elevate cybersecurity posture over time.

💡Key Takeaway

Enables strategic program growth by identifying long-term opportunities for maturing security practices.

🧭Choosing the Right Assessment(s)

There’s no one-size-fits-all approach. The right mix of assessments depends on your industry, operational risks, regulatory exposure, and current maturity level. The most effective organizations adopt a cyclical approach, assess, remediate, improve, and reassess.

🛡️The Champion Advantage

Champion combines deep OT expertise with proven cybersecurity practices. We tailor each assessment to your operational reality, ensuring recommendations are actionable, scalable, and aligned with your long-term goals. Our comprehensive approach uncovers risks that others miss and delivers practical solutions that enhance operational resilience.

👉Get Started

Ready to evaluate your OT cybersecurity posture? Understanding the types of assessments is the first step. Let Champion guide you from insight to action, ensuring your systems remain secure, compliant, and future-ready.

Let's collaborate.

Schedule a no-cost consultation today.


article

Navigating New MTSA Cybersecurity Regulations


More Posts

Read More
Article

Safeguarding Your Expanding OT Assets: Maintaining & Securing IDCs

Expanding Footprint, Escalating Complexity: What's Next?

Industrial operational technology (OT) is evolving fast. Once-isolated systems now rely on interconnected virtual machines, edge devices, software agents, and cloud connectors. At the center of this transformation sits the Industrial Data Center (IDC), the control hub for real-time operations, data acquisition, and analytics.

But with greater digitalization comes a challenge: How do you maintain and secure your IDC in a scalable, reliable, and cost-effective way?

It starts with moving beyond traditional IT approaches and adopting frameworks built specifically for OT environments.

What Makes IDCs Different?

Unlike enterprise data centers, IDCs operate in high-stakes environments where uptime is non-negotiable. A failure isn’t just an IT issue, it can halt production, cause safety incidents, or trigger regulatory violations.

IDCs in critical infrastructure sectors demand special attention in four key areas:

  • Operational Continuity: Real-time control requires zero latency and uninterrupted uptime.
  • System Reliability: All components, hardware and software, must perform predictably.
  • Legacy Integration: OT systems often blend decades-old tech with new platforms.
  • Cyber-Physical Risk: Digital breaches can cause real-world harm.

Three Pillars of IDC Reliability & Security

1. Infrastructure Resilience for OT Uptime

Reliability begins with the physical and virtual backbone of the IDC:

  • Hardware Redundancy: Use failover-ready servers, networks, and storage to eliminate single points of failure.
  • Component Health Monitoring: Proactively monitor CPUs, memory, storage, power, and network performance to identify issues before they impact operations.

2. Cybersecurity Built for Converged OT/IT Environments

Cyber threats don’t stop at the firewall and in OT, they can be catastrophic:

  • Network Segmentation: Isolate OT networks (e.g., control, historian) to contain breaches and reduce risk.
  • Patch Management: Develop OT-specific strategies that prioritize safety, vendor compatibility, and availability.
  • Endpoint Security: Secure all IDC assets, servers, workstations, devices, with antivirus, firewalls, and intrusion detection.
  • IAM & Remote Access Control: Enforce least-privilege, MFA, and regular access audits.
  • Vulnerability Management: Continuously assess and remediate weaknesses in software, firmware, and configurations.

3. Proactive Monitoring & Lifecycle Governance

Resilient systems don’t just react, they anticipate:

The Champion Advantage

For organizations modernizing their OT backbone, Champion Technology Services offers deep experience in building and securing IDCs in high-risk industrial sectors. From hazardous midstream operations to specialty chemical plants, we deliver:

  • Turnkey Infrastructure Solutions— From power and cooling to server and storage design
  • Secure Network Architectures— Segmented, fault-tolerant, and built for OT
  • Integrated Cybersecurity Controls— Aligned with industry standards like ISA/IEC 62443
  • Lifecycle & Modernization Planning— Keeping your systems future-ready

Let's collaborate.

Schedule a no-cost consultation today.


Solution Brief

Industrial Data Centers


More Posts

Read More
Article

Scalable Strategies for OT Asset Management

More Assets, More Complexity, Now What?

Industrial operations today are not just adding hardware, they’re layering in virtual machines, edge devices, software agents, and cloud connectors. With this growth comes the challenge: how do you manage all these assets reliably, securely, and cost-effectively at scale?

The answer lies in combining monitoring with structured asset management strategies.

Strategy 1: Establish a Baseline with Passive Discovery

Before you can manage, you need visibility.

  • Start with Passive Monitoring tools to automatically detect devices communicating across your network. 
  • Build an initial asset inventory that includes IP, MAC, vendor, model, and firmware.
  • Capture not just what’s online, but what’s vulnerable, misconfigured, or behaving abnormally. 

Tip

Passive monitoring can often be deployed with zero impact to operations and works across diverse platforms.

Strategy 2: Tag & Contextualize Assets 

An inventory without context is just a list.

  • Tag assets with critical metadata—such as control zone, site, function (e.g., HMI,DCS, historian), and ownership. 
  • Link this data with existing sources: CMMS, control system configuration, historian, or network diagrams.
  • Use human-friendly naming conventions and hierarchy to support operational handoffs and audits. 

PRACTICAL STEP

Use spreadsheet imports, CMDB tools, or open API integrations to enrich your inventory without manual re-entry.

Strategy 3: Integrate Monitoring with Lifecycle Planning 

Monitoring tells you what’s happening—asset management tells you what to do next.

  • Leverage performance data to flag aging or underperforming assets.
  • Track lifecycle stages: install date, firmware version, last patch, end-of-support.
  • Schedule reviews for high-risk systems or those approaching obsolescence.

bonus

If you’ve recently migrated to a modern system, start lifecycle tracking from day one to maximize ROI.

Strategy 4: Build Change Management into Daily Operations

Static inventories go stale fast.

  • Monitor for unauthorized changes in firmware, configuration, or IP address.
  • Tie changes to maintenance work orders or authorized updates.
  • Use alerts to notify engineering or cybersecurity teams when anomalies occur.

Scalable Tactic

Focus on key control zones first, then expand visibility zone by zone, prioritize based on risk and asset count.

Strategy 5: Make It Actionable for the Teams Who Need It

The most successful OT asset strategies are ones that are used daily.

  • Build dashboards that serve operators, not just auditors.
  • Align asset groups with how your team works, by process area, shift, or system owner.
  • Offer read-only access to contractors or support teams to eliminate bottlenecks.

TOOLTIP

Integrate with your existing FAT documentation, virtual environments, or support models like our 24UP® Solution, to make data available in context.

Conclusion: OT Asset Management is a Discipline, Not a Project

Scalability doesn’t come from a one-time cleanup, it comes from embedding asset practices into monitoring, maintenance, and modernization. Whether you’re managing 100 devices or 10,000, the right strategy allows your team to grow confidently alongside your infrastructure.

Let's collaborate.

Schedule a no-cost consultation today.


Solution Brief

Asset Management


More Posts

Read More
Article

OT Asset Management: A Key Pillar in MTSA Cybersecurity Compliance

As cybersecurity regulations under the Maritime Transportation Security Act (MTSA) expand to cover Operational Technology (OT), many facility operators are asking a critical question: "Do we really know what assets we're protecting?"
The answer often reveals a blind spot.
According to industry data, over 70% of organizations lack a comprehensive OT asset management strategy. This gap doesn’t just hinder performance—it puts entire facilities at risk of non-compliance, operational downtime, and cyber threats.
That’s where Champion comes in.

📊 Asset Management: Your First Line of Defense

Our scalable OT asset management solutions are built to enhance visibility, secure legacy systems, and support compliance with new MTSA requirements. By continuously discovering, classifying, and monitoring assets across your OT environment, Champion helps reduce risk and build the digital foundation for long-term resilience.

We combine:

  • Up-to-date dashboards to unify asset KPIs and vulnerabilities
  • Lifecycle-based risk prioritization to streamline response
  • 24/7 expert support from seasoned OT cybersecurity professionals

Whether you're preparing your Facility Security Plan or responding to an audit, knowing what’s in your environment—and how it behaves—is step one.

🚀 Ready for MTSA and Beyond

Champion doesn’t just help you check compliance boxes. We help you build a cyber-smart asset strategy that scales with your operations and aligns with MTSA mandates like:

  • Continuous cyber risk assessments
  • OT-specific incident response plans
  • Network segmentation and supply chain visibility

Let’s close the visibility gap—before it becomes a security gap.

Let's collaborate.

Schedule a no-cost consultation today.


Solution Brief

Asset Management


More Posts

Read More
Article

Navigating New MTSA Cybersecurity Regulations

With cybersecurity threats growing more advanced and persistent, regulatory bodies are raising the bar, especially across critical infrastructure sectors. For facilities covered under the Maritime Transportation Security Act (MTSA), the U.S. Coast Guard is introducing new cybersecurity requirements that demand immediate attention.

As a trusted leader in Operational Technology (OT) cybersecurity, Champion Technology Services is here to guide you through this evolving compliance landscape and help strengthen your organization’s cyber resilience.


What’s Changing with MTSA?

The Maritime Transportation Security Act (MTSA) historically focused on physical security. Recent updates expand its scope to include cybersecurity risk management requirements for MTSA-regulated facilities. These changes reflect increasing attention to vulnerabilities within systems that support maritime operations, including industrial control systems (ICS), SCADA platforms, and connected operational technologies.

Key upcoming requirements include:

  • Integration of cybersecurity controls into Facility Security Plans (FSPs)
  • Routine cyber risk assessments
  • Development of Incident response plans  addressing OT-related cyber events threats
  • Ongoing training and incident response exercises
  • Demonstration of supply chain cybersecurity awareness and risk management

Why It Matters to OT Environments

Unlike traditional IT systems, OT environments often rely on long lifecycle infrastructure and specialized industrial protocols, which can make them more complex to secure and modernize.

OT environments face growing exposure to cybersecurity risks including:

  • Operational disruption caused by ransomware or other malicious activity
  • Targeted cyber activity affecting critical infrastructure sectors
  • Vulnerabilities within industrial control system software and firmware

These updated MTSA regulations highlight a broader shift: OT cybersecurity is now a core component of operational risk management and regulatory compliance.

How Champion Can Help

Champion helps organizations bridge the gap between regulatory compliance and practical OT cybersecurity implementation. Meeting these requirements requires both regulatory understanding and practical OT cybersecurity experience.  Here’s how we can support your MTSA compliance journey:

1. Cybersecurity Risk Assessments

We evaluate your OT environment using standards like NIST CSF, IEC 62443, and USCG directives, identifying gaps and vulnerabilities.

2. FSP Cybersecurity Integration

We update or develop Facility Security Plans to meet evolving Coast Guard expectations—grounded in real-world OT constraints.

3. Secure Network Architecture

Champion engineers design resilient network infrastructures, including:

  • Industrial Firewalls
  • Industrial DMZ architectures
  • Secure remote access solutions
  • VLAN segmentation and network zoning

4. OT-Focused Incident Response

We co-develop incident response playbooks tailored to OT systems—minimizing downtime and speeding up recovery.

5. Training and Simulation

Through hands-on workshops and tabletop exercises, we help OT personnel develop the skills needed to identify, respond to, and report cybersecurity incidents.

6. Managed OT Security Services

Stay protected 24/7 with Champion’s monitoring, threat detection, and vulnerability management—purpose-built for industrial environments.

The Champion Advantage

We bring decades of experience across energy, manufacturing, terminals, and critical infrastructure sectors—where compliance and uptime are non-negotiable. Our team combines deep OT knowledge with practical cybersecurity expertise, ensuring your path to MTSA compliance is structured, practical, and aligned with operational realities.

Final Thoughts

These MTSA updates represent an important evolution in how maritime and industrial operators approach cybersecurity and operational resilience. Let Champion Technology Services help you:

✅ Understand the new rules
✅ Achieve compliance
✅ Build cyber resilience for the future

Champion ready to help you navigate the MTSA cybersecurity requirements with confidence.

Let's collaborate.

Schedule a no-cost consultation today.


more on our website

Industrial Cybersecurity


More Posts

Read More
Article

Has your facility taken steps to prevent unnecessary downtime?

You may have experienced it before:
  • Your operator experiences an abnormal situation that costs you production time, and your in-house staff is too busy to identify the REAL root cause.
  • Extended downtime because a critical part of your control system fails and you don’t have a replacement.
  • You are striving for maximum uptime and production, but your control system is not allowing you to reach your goals.
  • Your control system reaches end-of-life and you can’t get support.
The list goes on. How can you proactively address these issues while ensuring that your control system is not an impediment in reaching your goals?

Partnership with a solution provider may be the key

24UP® Solutions is Champion’s premier Industrial Control System, Operational Technology, and Industrial Cybersecurity solution led by the experts who have seen it all. Clients rely on 24UP® to ensure a proactive response to issues that often arise, but are often not considered – or simply haven’t had the time to address.

Whether simply providing you with the tools to be prepared for unexpected challenges, or being your primary provider of maintenance and 24/7 emergency support – we work with you to tailor a plan that fits your needs and budget. Your company’s 24UP® Solutions could include your highest need to help you achieve your goals, including:

  • PREVENTIVE MAINTENANCE such as routine Control System hardware and OT system diagnostics, backups, and imaging, and other preventative maintenance services
  • ASSET MANAGEMENT such as critical spare parts assessments, inventory, and the services to replace the parts that keep you up at night
  • 24/7 SUPPORT for general maintenance or simply staff augmentation to provide reliability and flexibility
  • CYBERSECURITY MAINTENANCE services such as scheduled audits to help identify your OT system vulnerabilities and implement solutions to protect you from the ever evolving cyber threats
  • PROCEDURE & DOCUMENTATION to enable your team to perform simple control system maintenance without formal training

Let's collaborate.

Schedule a no-cost consultation today.


more on our website

24UP® Solutions


More Posts

Read More