MTSA

Phase 3: Reporting & Training

Phase 3: Reporting & Training

Validate cybersecurity measures and establish ongoing compliance

Controls only count if they hold under pressure and under audit. Phase 3 tests what you've built, keeps documentation current, and proves your team can respond when something goes wrong.

What You Get

  • OT appropriate penetration testing and validation
  • Annual audit support and Cybersecurity Plan updates
  • Tabletop exercises and required drills
  • Recurring risk assessments and training delivery
Read More
MTSA

Phase 2: Risk Assessment & Controls

Phase 2: Risk Assessment & Controls

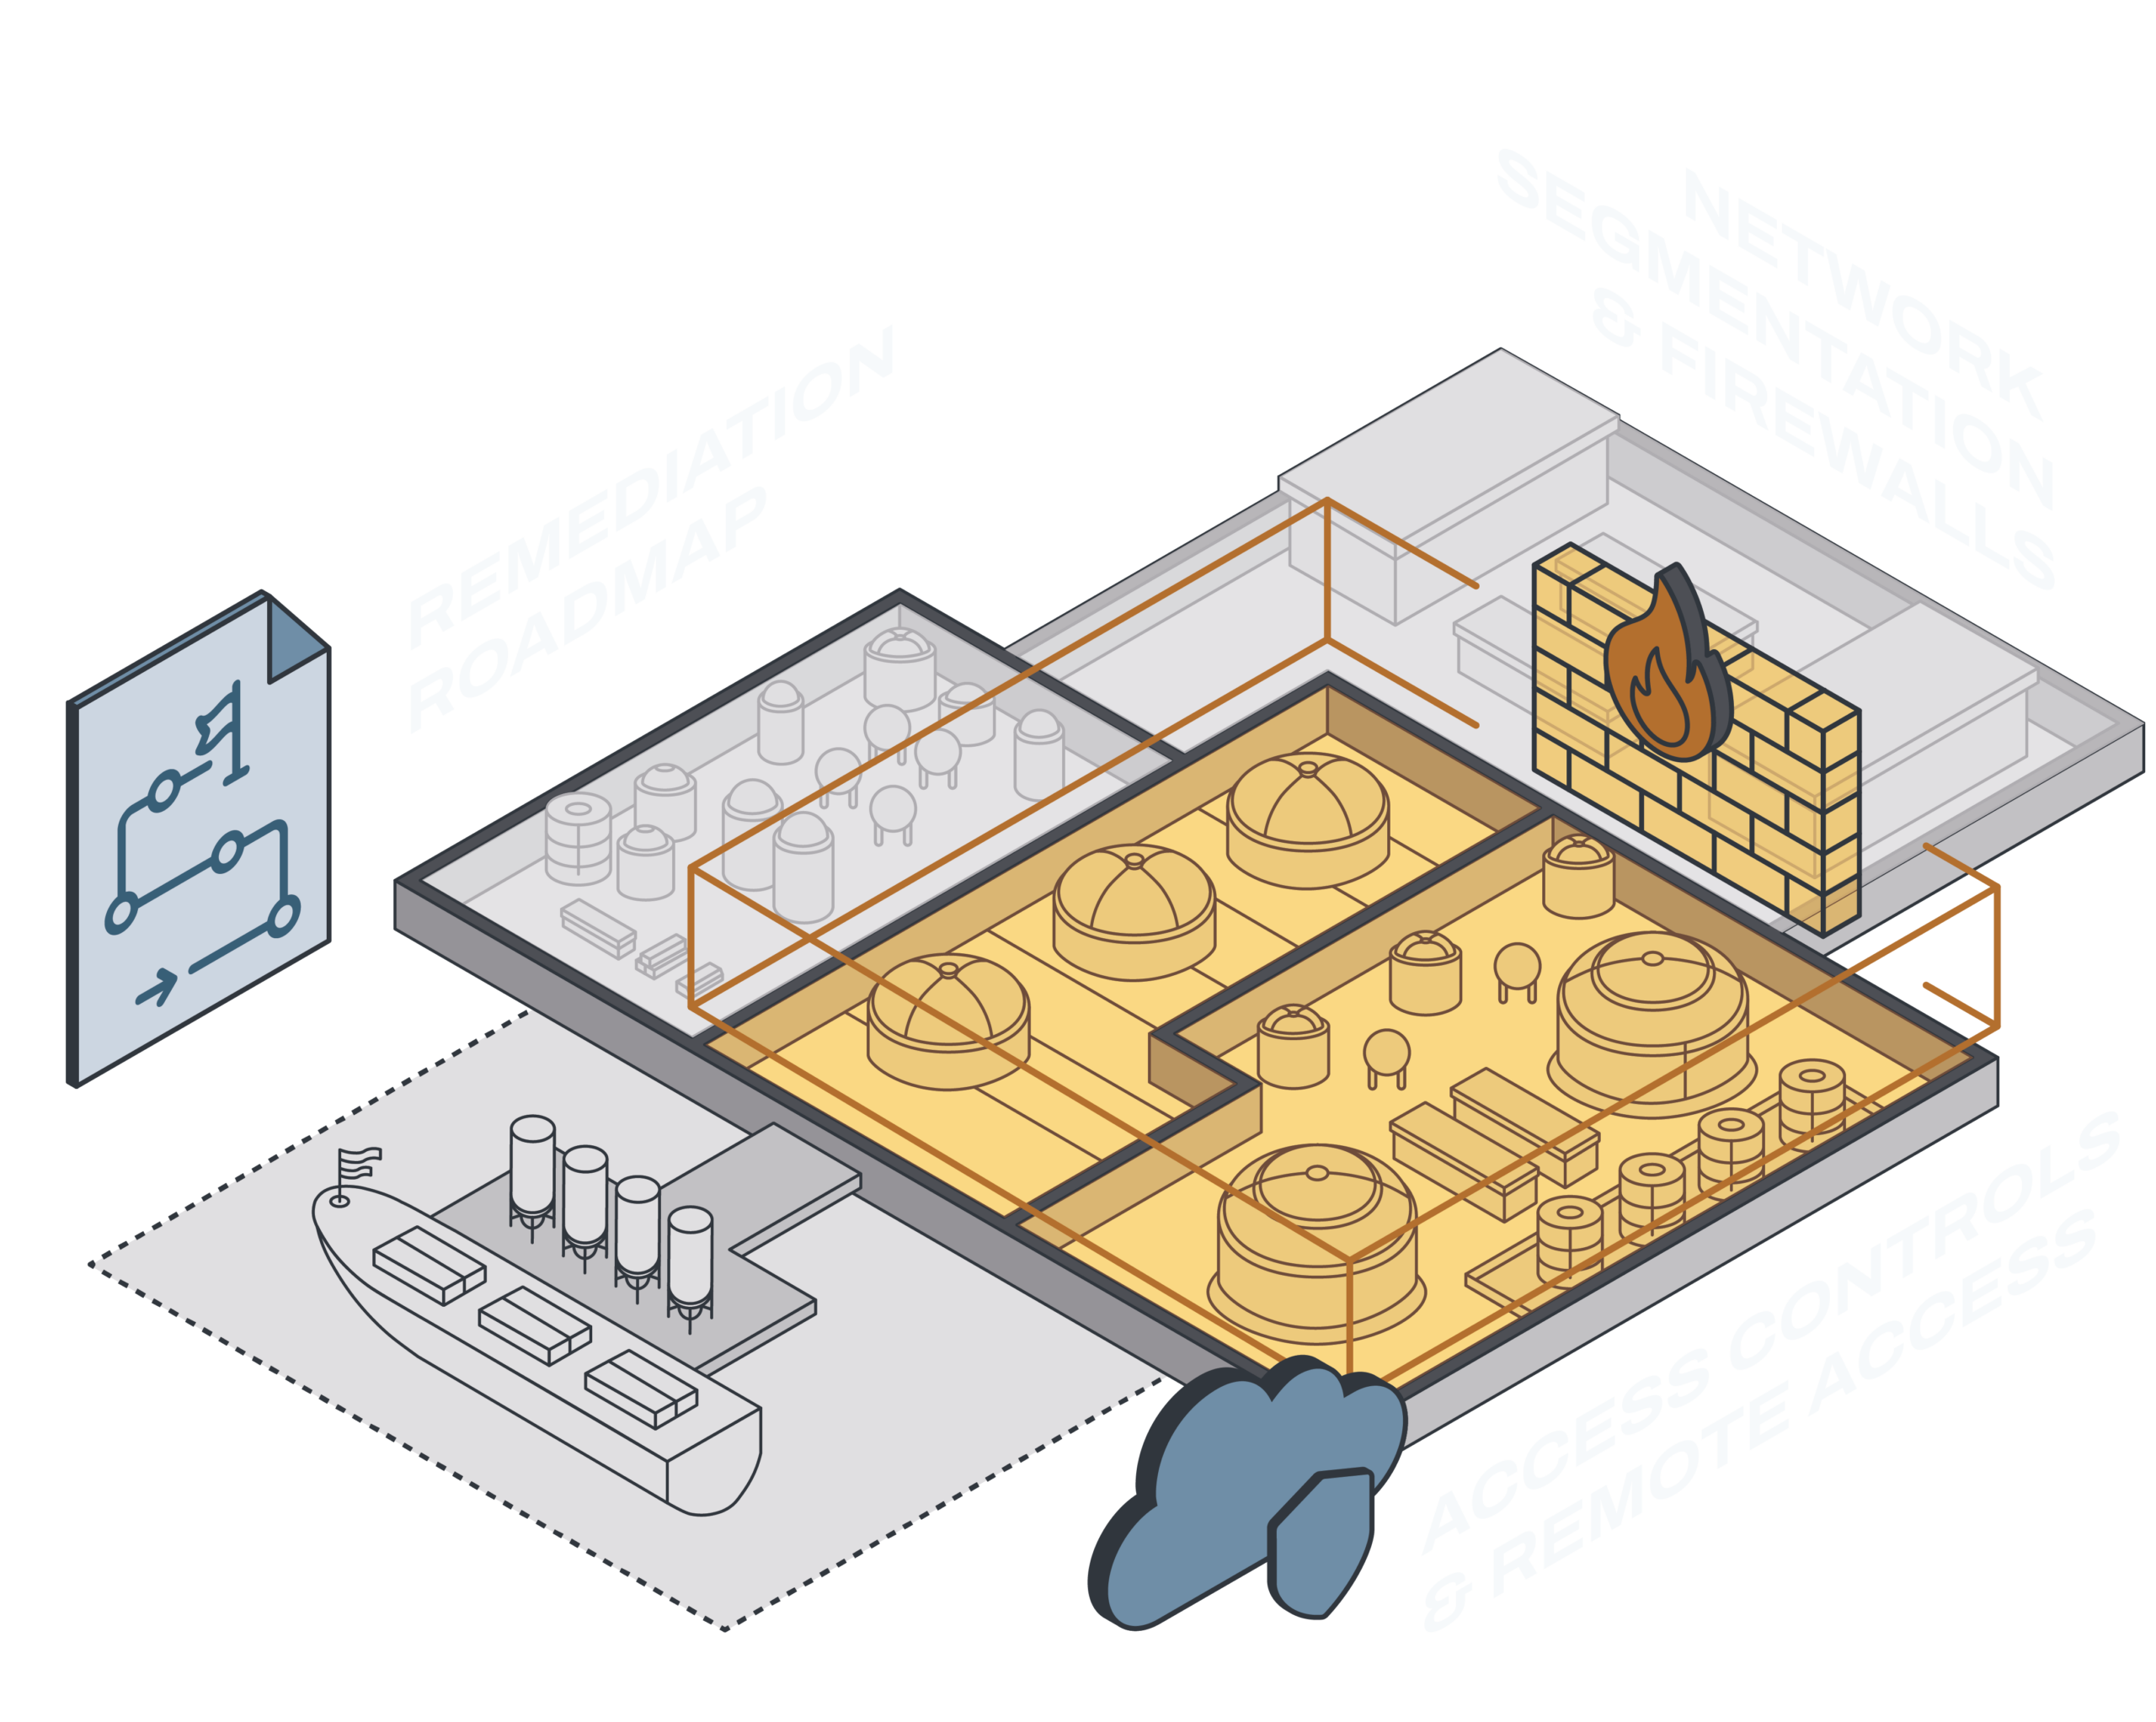
Turn identified risks into a practical path forward

A gap analysis is only useful if someone closes the gaps. Phase 2 turns assessment findings into a written Cybersecurity Plan and implements the controls behind it, sequenced around your production windows.

What You Get

  • Written Cybersecurity Plan meeting MTSA submission requirements
  • Prioritized remediation roadmap sequences around production windows
  • Network segmentation and firewall
  • Secure remote access and account control implementation
Read More
MTSA

Phase 1: Reporting & Training

Phase 1: Reporting & Training

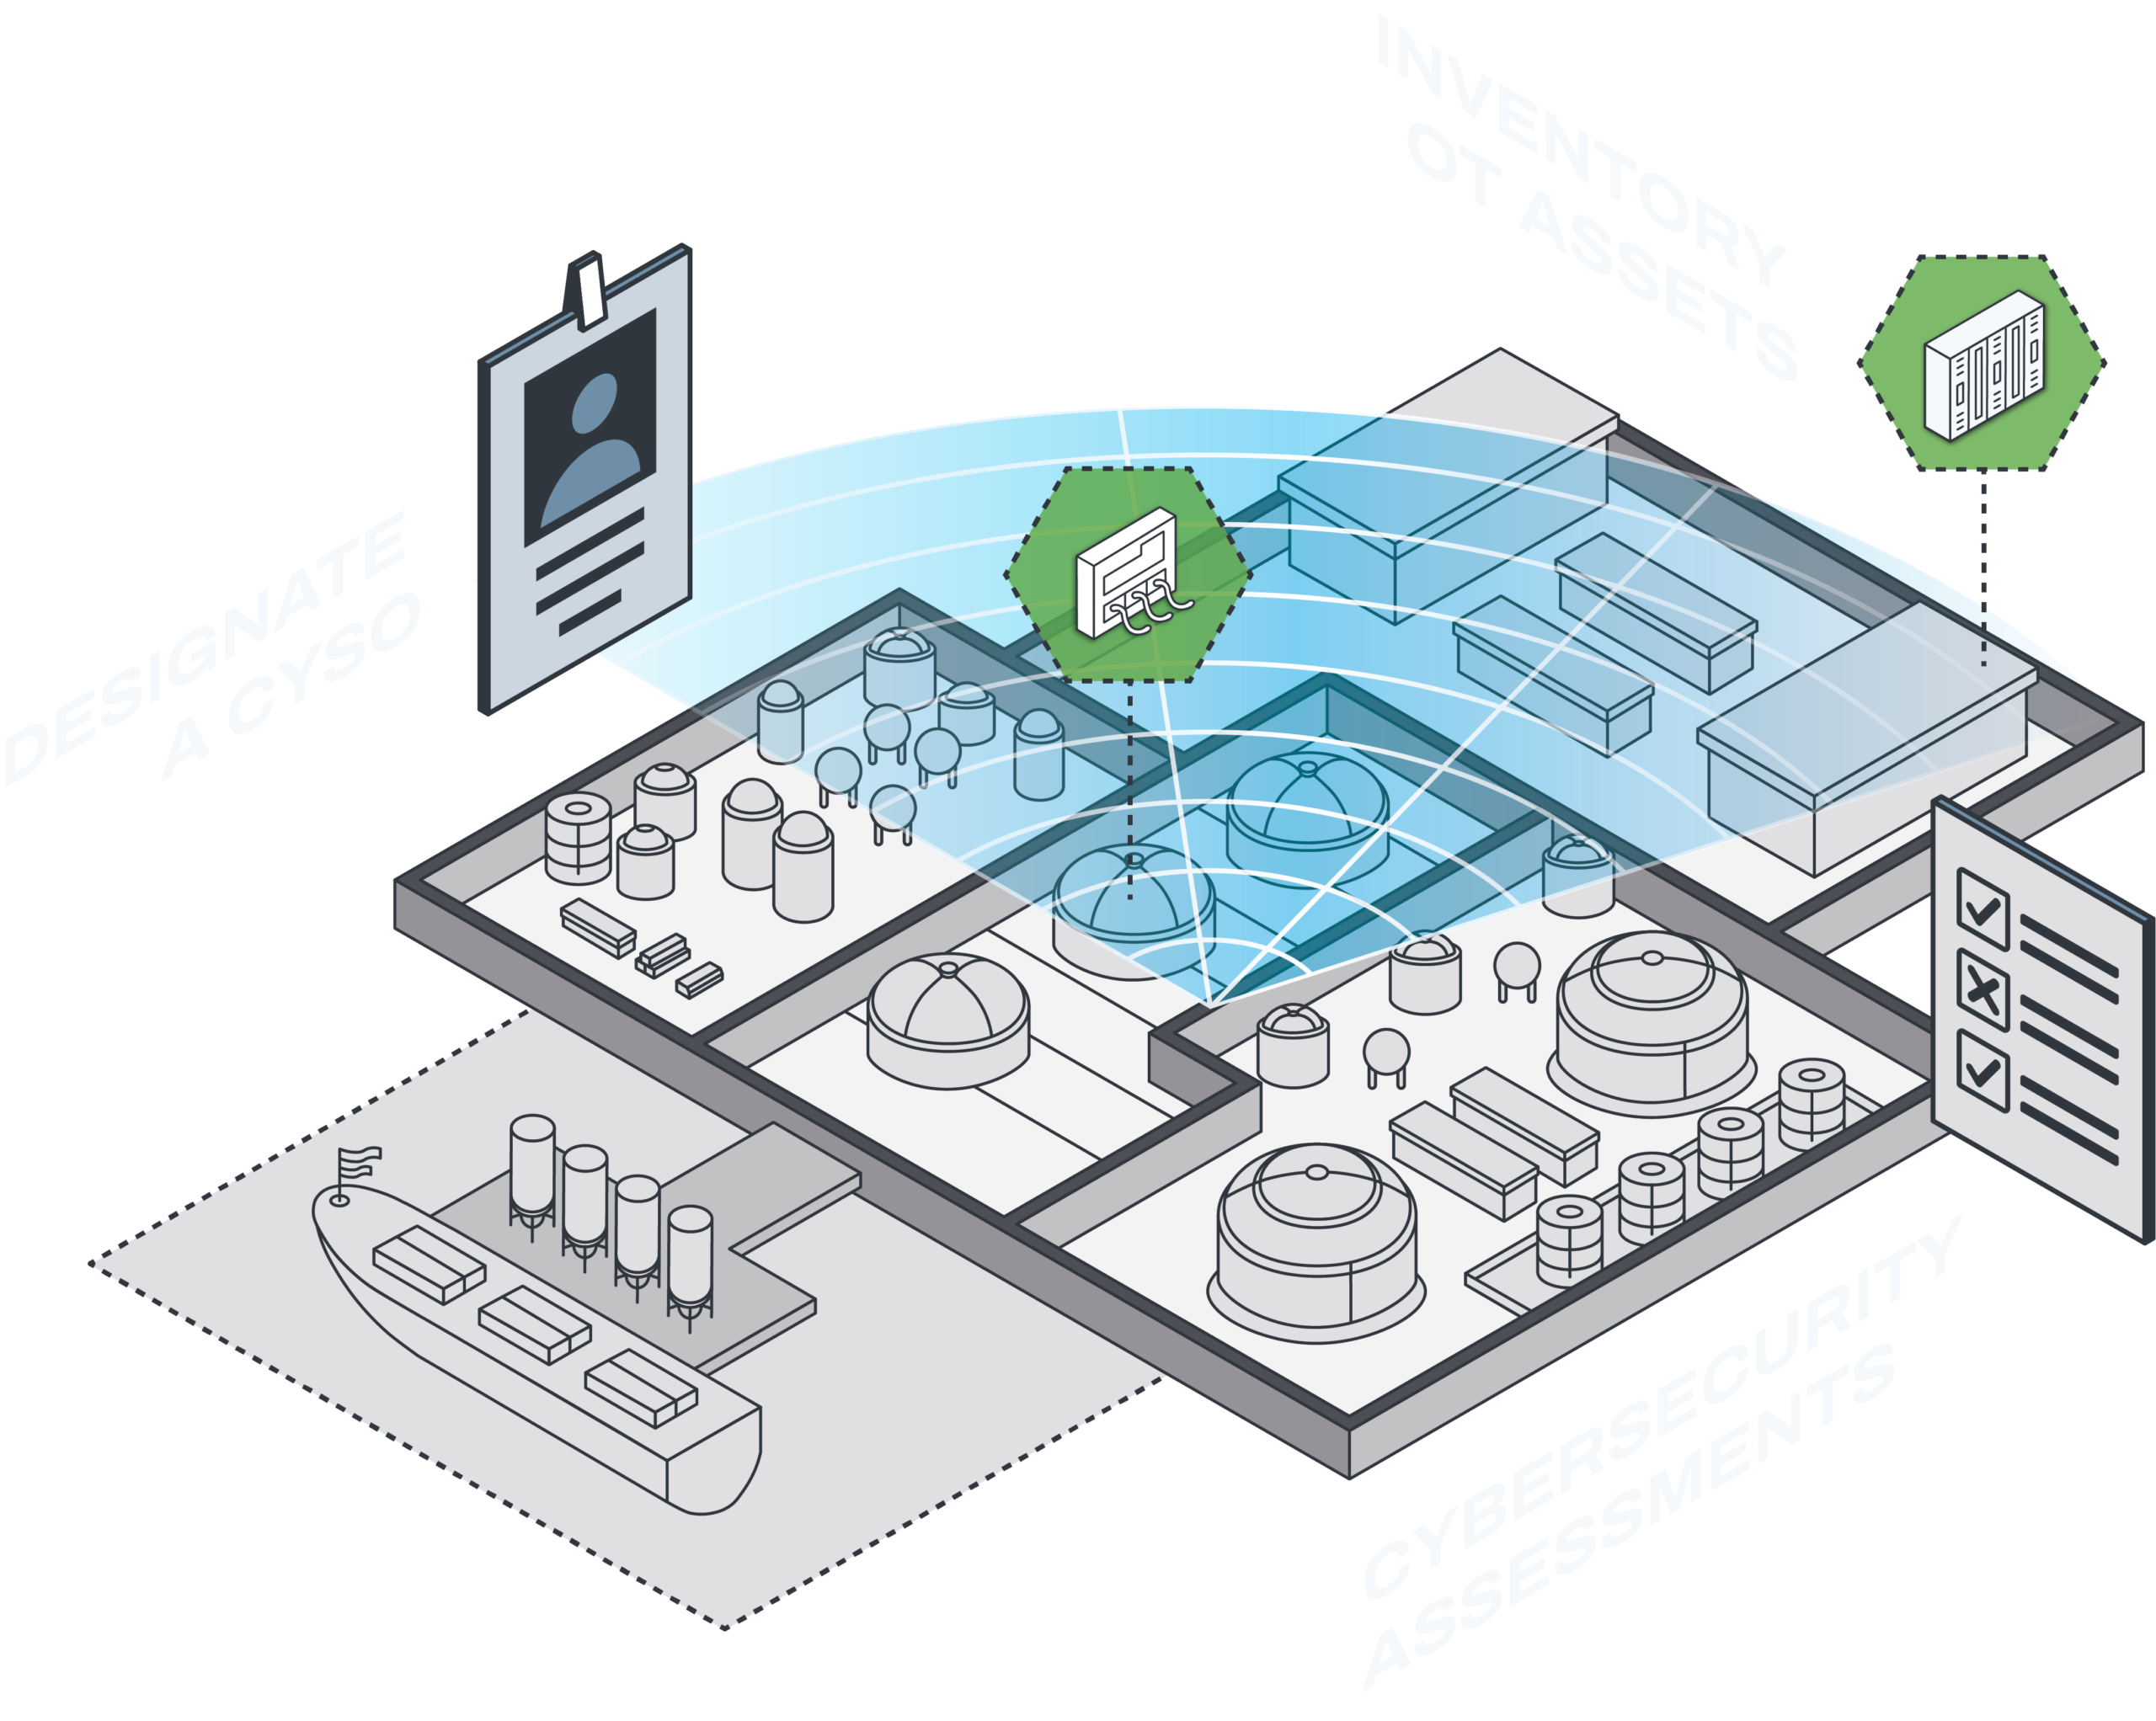
Establish the foundation for MTSA cybersecurity compliance

You can't secure what you haven't inventoried. Phase 1 designates your Cybersecurity Officer, maps your OT assets, and completes the site-specific assessment the rule requires.

What You Get

  • Cybersecurity Officer designation and defined responsibilities
  • OT asset Inventory across DCS, SCADA, PLC, and safety systems
  • Site specific Cybersecurity Assessment
  • Gap analysis mapped to MTSA account security, device security, training, and incident reporting requirements
Read More
Article

Compliance Assessments Made Practical

Navigating today’s cybersecurity regulations can feel overwhelming, especially in industrial environments where operational realities add complexity.

A compliance assessment cuts through that noise by answering a critical question: are we truly meeting our regulatory requirements?

It’s not just about avoiding fines. It’s about building a structured, auditable security program that aligns with recognized standards and stands up to real-world scrutiny.

A compliance assessment evaluates your organization’s alignment with established frameworks such as ISA/IEC 62443, NIST Cybersecurity Framework (including ICS guidance), and NERC CIP. It compares your existing controls, processes, and documentation against required standards, clearly identifying where you meet expectations and where gaps remain.

Why It Matters in Industrial OT

For industrial organizations, compliance is no longer optional, it’s operationally critical.
Cyber incidents in OT environments don’t just impact data, they can disrupt production, impact safety, and create regulatory exposure. At the same time, evolving mandates (such as MTSA updates and sector-specific regulations) are increasing expectations for demonstrable cybersecurity maturity.

A compliance assessment ensures you are not only prepared for audits but are also building a defensible, resilient security posture. It shifts compliance from a checkbox exercise to a sustainable operational capability.

Key Components

Policy and Documentation Review

We evaluate your existing policies, procedures, and supporting documentation, from incident response to asset management. The goal is to ensure documentation is not only present, but accurate, actionable, and aligned with the target framework.

Technical Control Evaluation

Compliance doesn’t stop at documentation. We validate that technical controls are implemented and functioning as intended, reviewing segmentation, access controls, firewall configurations, and system hardening within the realities of an OT environment.

Regulatory Gap Identification

We perform a structured gap analysis to identify where your current posture diverges from required standards. The output is a clear, actionable roadmap, not just a list of deficiencies.

Remediation Planning

Closing gaps requires more than recommendations. We work alongside your team to prioritize actions based on risk, operational impact, and compliance urgency, balancing security improvements with production continuity.

Making Compliance Practical in OT

Compliance in OT isn’t always straightforward. Legacy infrastructure, uptime requirements, and safety considerations make traditional IT-driven approaches difficult to apply in practice.
A successful compliance program must account for how industrial systems actually operate, where changes must be carefully planned, validated, and executed without disrupting production.
This is where experience matters. Translating regulatory requirements into real-world implementation, while maintaining operational continuity, is what ultimately determines success.

Key Takeaway 

A compliance assessment provides clarity in a complex regulatory landscape. It establishes a defensible baseline, identifies what matters most, and creates a path forward.

Done right, it’s not just about passing an audit, it’s about building a program that is repeatable, sustainable, and aligned with how industrial operations actually run.

  • The Champion Advantage

Champion brings a practical, execution-focused approach to OT compliance, bridging the gap between regulatory requirements and operational reality.

OT-Native Expertise

Deep experience across control systems, networks, and industrial processes ensures recommendations are grounded in real operations. 

Operationally Safe Execution

Solutions are designed and validated with uptime, safety, and production constraints in mind. 

End-to-End Support

From assessment through remediation and ongoing support, we stay engaged to ensure outcomes—not just deliverables. 

Aligned with Modernization Efforts

Compliance is integrated into broader initiatives such as system upgrades, network redesigns, and cybersecurity improvements.

This approach is demonstrated in real-world projects, such as control system upgrades and network modernization executed without operational disruption, where compliance, reliability, and performance are advanced together.


Ready to learn more? Contact us today to schedule a no-cost consultation.

We empower our clients to build safe, sustainable operations by delivering comprehensive Operational Technology (OT) solutions. From concept to implementation and beyond– we'll be there every step of the way.

Solution Brief

MTSA Cybersecurity Compliance


Let's collaborate.

Schedule a no-cost consultation today.


More Posts

Read More
Cybersecurity Phases

Monitor & Sustain


Continuous monitoring, patch and lifecycle management, and OT specialist support through 24UP®, so the security posture holds after the project closes.

What Changes on Site
  • Continuous monitoring with OT-contextual alerting
  • Ongoing vulnerability and patch management
  • Backup validation and periodic recovery testing
  • Remote and on-site OT and Control System specialists on call
Read More
Cybersecurity Phases

Remediate & Implement


Segmentation, hardening, secure remote access, and backup recovery, executed for in production systems, scheduled around your operations without always requiring a shutdown.

What Changes on Site
  • Network segmentation between process and business networks
  • Secure remote access replacing shared or unmanaged connections
  • Hardened systems with a patch process that fits OT constraints
  • Validated backups with tested recovery procedures
Read More
Article

OT Vulnerability Assessments: Turning Visibility into Action

While a gap or risk assessment provides a strategic view of your overall security posture, an OT vulnerability assessment delivers a granular, technical snapshot of where your systems are most exposed. It is a proactive, systematic process that combines OT-aware automated tools with expert manual analysis to identify, classify, and prioritize known vulnerabilities across networks, assets, and applications, such as unpatched software, insecure configurations, and legacy design flaws, that could be exploited by a malicious actor.

The goal is simple but critical: find and address vulnerabilities before they are leveraged against your operations.

Why It Matters

In industrial environments, vulnerability assessments are a core component of proactive asset and security management, not just a cybersecurity exercise. Unlike IT systems, OT assets often run continuously, support safety-critical processes, and may rely on legacy hardware or operating systems that cannot be easily patched or replaced.

A thorough OT vulnerability assessment goes beyond software flaws to uncover: 

  • Misconfigurations that weaken defense-in-depth 
  • Unsupported or unpatched systems increasing cyber and operational risk
  • Insecure access pathways that could lead to a cyber-physical incident 

Left unaddressed, these vulnerabilities increase the likelihood of unplanned downtime, safety incidents, and loss of operational control.

Key Components

Automated Scanning 

Specialized, non-intrusive OT-aware tools are used to identify known vulnerabilities across networks, devices, and applications, such as missing patches, insecure services, or default credentials. Scanning is carefully planned and executed to avoid disrupting sensitive control processes.

Manual Review 

Expert engineers perform in-depth reviews of system configurations, network architectures, access controls, and operational practices. This human analysis is essential in OT environments, where context matters and automated tools alone may overlook logical design flaws or risk-creating exceptions.

Physical Security Inspection 

In OT environments, cyber risk often starts with physical access, intentional or accidental. On-site inspections identify physical exposure points such as unsecured cabinets, control panels, removable media access, or network drops, making physical security a critical component of a true OT vulnerability assessment.

Reporting and Prioritization 

Findings are documented in a clear, actionable report that:

  • Assigns severity based on operational and safety impact 
  • Differentiates between vulnerabilities that can be patched, mitigated, or accepted
  • Provides practical remediation guidance aligned with plant constraints 

Results are prioritized collaboratively so teams can focus first on vulnerabilities that pose the greatest risk to safety, reliability, and uptime.

Key Takeaway 

An OT vulnerability assessment is the operational backbone of proactive security. It transforms abstract risk into a prioritized, actionable list of technical and physical weaknesses that can be addressed through targeted remediation. By systematically reducing exposure, organizations shrink their attack surface, improve resilience, and make industrial systems far more difficult to compromise, without disrupting operations.

  • The Champion Advantage

Champion’s OT vulnerability assessments are designed specifically for live, safety-critical industrial environments, where uptime, process integrity, and operator confidence matter as much as cybersecurity.

OT-First, Operations-Aware Execution

Our assessments are led by engineers with deep control system and plant operations experience, not IT-only security teams, ensuring vulnerabilities are identified without disrupting production.

Contextual Risk Prioritization

Vulnerabilities are evaluated based on real operational impact, safety, reliability, environmental risk, and downtime, not just generic CVSS scores.

Actionable, Realistic Remediation Guidance

Our recommendations reflect operational constraints such as patch windows, vendor support limitations, and system life cycle considerations, providing practical mitigation paths, not theoretical fixes.

Safe, Non-Intrusive Assessment Methods

We use OT-approved tools and carefully planned techniques tailored to industrial protocols and legacy systems, minimizing risk to sensitive processes and equipment.

Integrated Cyber-Physical Perspective

By combining network analysis, configuration review, and physical security inspection, we uncover attack paths that purely digital assessments often miss.

Built to Feed the Broader OT Security Roadmap

Vulnerability assessment results seamlessly support gap assessments, risk analysis, segmentation design, and long-term modernization planning, turning findings into sustained improvement.

With Champion, OT vulnerability assessments are not a one-time scan, they are a disciplined, operations-safe process that protects what matters most: safe and reliable operations.

Secure the Foundation, Modernize with Confidence

Modernizing on top of hidden security flaws is a recipe for future downtime. A Vulnerability Assessment provides a technical "deep dive" into your assets before you start major modernization project like:

  • On-Process Migrations
  • OT Data Center Development
  • Virtualization
  • Network Redesigns

By purging known vulnerabilities early, you ensure your new system is built on a clean, stable, and secure foundation.

Let's collaborate.

Schedule a no-cost consultation today.


Article

A Guide to Cybersecurity Assessments


More Posts

Read More
Cybersecurity Phases

Assess & Prioritize


Discover every OT asset and communication path, then rank risk by operational impact rather than CVSS score. Findings come with a remediation roadmap, not just a list.

What Changes on Site
  • Complete OT asset inventory with communication mapping
  • Risk ranking weighted by process criticality and safety impact
  • ISA/IEC 62443-aligned assessment against your actual architecture
  • Prioritized remediation roadmap with effort and sequencing
Read More
Article

Gap Assessments: Your Security Starting Point

OT Cybersecurity Gap Assessments: The First Step Toward a Safer, More Reliable Operation 

For industrial organizations, building a mature cybersecurity posture starts with clarity. You can’t improve what you can’t see, especially in complex OT environments where aging systems, undocumented devices, and day-to-day operational pressures create blind spots. 

A gap assessment gives OT teams that clarity. By comparing your current controls, policies, and procedures against frameworks like NIST CSF, ISA/IEC 62443, or NERC CIP, it delivers a clear, prioritized roadmap tailored to your operations. For operators, technicians, and engineers, the impact is direct: improved uptime, reliability, safety, and long-term system health. 

What an OT Gap Assessment Is and Why It Matters 

A gap assessment evaluates your OT environment against a defined target state built on industry standards, regulatory requirements, and operational needs. It enables you to understand: 

  • Your true security posture 
  • Operational weaknesses tied to legacy systems or manual processes 
  • Misalignments between policy and reality 
  • The highest-impact improvements to reduce risk 

OT systems can’t simply be rebooted or patched whenever convenient. Every change must protect safety, reliability, and process continuity and a gap assessment ensures your controls and processes support those realities. 

For OT personnel, the benefits include: 

  • Better visibility into aging and undocumented assets 
  • Reduced troubleshooting time 
  • Increased confidence in system reliability 
  • Early insight into modernization and lifecycle requirements 
  • Stronger justification for budget and resource planning 

A gap assessment shifts the conversation from “Is our firewall configured correctly?” to “Do our systems and processes support long-term operational health and safety?”

What to Expect During the Assessment 

The process is collaborative and designed to minimize operational disruption. It focuses on how your facility actually works, not just what’s documented. 

Typical activities include: 

  • Documentation Review: Architecture diagrams, control system configurations, network designs, and backup procedures 
  • Field Validation: Walkdowns in control rooms, server cabinets, and field panels to verify what actually exists 
  • Workflow & Access Review: Operator practices, account usage, change management, and legacy “tribal knowledge” 

The goal is a clear, accurate understanding of your current environment. 

Key Components of an OT Gap Assessment 

1. Baseline Evaluation 

We document how systems are designed and operated today, capturing real-world conditions such as unsupported operating systems, end-of-life controllers, unmanaged network devices, vendor-installed assets, and manual processes that introduce operational risk. 

2. Target State Definition 

Together, we establish a realistic target state aligned with NIST CSF, ISA/IEC 62443, regulatory obligations, and your operational priorities. 

3. Gap Identification 

We highlight where your environment diverges from best practices across segmentation, access control, backups, patching, monitoring, governance, and system lifecycle practices and explain what each gap means for uptime, safety, and reliability. 

4. Remediation Planning 

We build a prioritized roadmap that accounts for downtime windows, staffing, investment needs, and alignment with ongoing modernization efforts. Every recommendation is practical for a 24/7 industrial environment. 

What We Typically Find and Why It Matters 

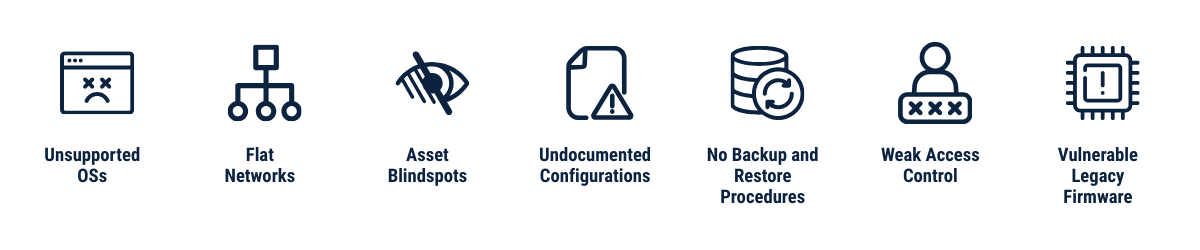
Across assessments, common issues include: 

  • Unsupported or unpatched operating systems 
  • Flat networks with limited segmentation 
  • Outdated or incomplete asset inventories 
  • Poorly documented configurations 
  • Lack of formal backup/restore procedures 
  • Shared accounts or unmanaged access 
  • Legacy firmware with known vulnerabilities 

These conditions are typical in long-lived OT systems. A gap assessment simply makes them visible so improvements can be planned objectively and cost-effectively. 

Key Takeaway 

A gap assessment is the foundational step toward building a resilient OT cybersecurity and operational program. It provides clarity, actionable priorities, and a realistic roadmap grounded in your operational reality. 

For OT end users, it delivers what matters most: safer operations, fewer disruptions, and a more reliable control system environment. 

🏆The Champion Advantage

We don't just assess, we also implement remediations. Many firms can identify gaps, Champion closes them. 

Deep OT Expertise 

Our engineers understand legacy and modern control systems across PLC, DCS, SCADA, networking, virtualization, and system architecture. 

From Findings to Implementation 

We don’t stop at recommendations. Our teams execute the remediation work, whether that means: 

  • Segmenting networks 
  • Deploying firewalls or access control improvements 
  • Updating or migrating control systems 
  • Virtualizing servers 
  • Implementing backup/DR solutions 
  • Replacing outdated PLCs or infrastructure 
  • Supporting DCS modernization or on-process migrations 

You get a partner who can take your roadmap from paper to production. 

Proven in Live Industrial Environments 

Our methodology has been refined across various critical infrastructure industries, without jeopardizing operational continuity. 

Integrated Support 

We work closely with operators, engineers, and IT/OT teams to ensure every improvement aligns with real workflows, staffing, and maintenance constraints. 

Your assessment becomes a fully supported execution plan, not homework. 

How Gap Assessments Support Modernization 

Many organizations begin with a gap assessment before embarking on broader modernization efforts like: 

  • DCS upgrades 
  • Virtualization 
  • On-process migrations 
  • Network redesigns 
  • OT data center development 

By identifying aging assets, unsupported software, and high-risk configurations early, the assessment ensures modernization plans are cleaner, safer, and more cost-effective.

Let's collaborate.

Schedule a no-cost consultation today.


Article

A Guide to Cybersecurity Assessments


More Posts

Read More
Article

Mastering OT Asset Monitoring

🛠️ Optimizing Uptime Through OT Monitoring

As industrial OT systems modernize and become more interconnected, the potential for efficiency and insight grows, but so do complexity and cybersecurity risk. To navigate this landscape, organizations must move beyond reactive maintenance and adopt a layered, proactive monitoring strategy.

🔍 Three Pillars of Modern OT Monitoring

Just as a skilled technician uses multiple tools to assess a system, a modern OT monitoring strategy relies on three complementary methods: passive, active, and predictive. When combined, they create a robust defense and operational advantage.

Passive Monitoring

The Silent Observer of OT Health

Passive monitoring silently collects data from systems without direct interaction. It captures the "background noise" of OT—CPU usage, network traffic, system logs—offering insights without introducing risk.

Use Cases:

  • Baseline Behavior: Define normal operating parameters to detect future anomalies.
  • Capacity Forecasting: Plan infrastructure scaling based on usage trends.
  • Performance Trends: Spot degradation or irregularities early.
  • Asset Visibility: Maintain a real-time inventory of connected OT assets.

Active Monitoring

Probing for Responsiveness and Resilience

Active monitoring takes a deliberate, hands-on approach. By sending test traffic or running diagnostics, it probes systems to detect weaknesses or performance bottlenecks.

Use Cases:

  • Early Issue Detection: Identify misconfigurations or failing components.
  • Network & Application Tuning: Support digital initiatives with optimized performance.
  • Cyber Vulnerability Scanning: Detect threats across newly connected assets.
  • Regulatory Readiness: Validate compliance with industry standards.

Predictive Monitoring

Anticipating What's Next

Predictive monitoring applies analytics and machine learning to historical and real-time data to forecast problems before they occur.

Use Cases:

  • Predictive Maintenance: Anticipate equipment failures and plan service proactively.
  • Resource Planning: Forecast compute and bandwidth needs as systems scale.
  • Anomaly Detection: Flag unusual activity that could signal cyber threats.
  • Downtime Reduction: Improve system uptime and reliability through foresight.

⚖️ Why the Blend Matters

Each technique brings value, but together they form a resilient and intelligent monitoring ecosystem:

  • Passive reveals system norms and long-term trends.
  • Active exposes immediate issues and security gaps.
  • Predictive enables preemptive action to avoid disruptions.

Conclusion

In a digital-first OT landscape, monitoring must evolve. A layered strategy, passive for visibility, active for control, and predictive for foresight, empowers industrial organizations to maintain uptime, ensure security, and drive operational excellence. It’s not just about watching your systems; it’s about truly understanding them.
more on our website

24UP® Solutions


Let's collaborate.

Schedule a no-cost consultation today.


More Posts

Read More